Manufacturers must report actively exploited vulnerabilities and severe incidents to ENISA and national CSIRTs.
Timelines: 24-hour early warning, 72-hour detailed notice, and 14-day final report.
This applies to all products currently on the market, not just new models.
As an Open Source developer spending my free time and free will and is not compensated by BeagleBoard.org. (I also live in North Dakota, a non EU territory). Consider me under the “Software Exceptions” listed as:
Non-Commercial Open Source: Free-of-charge software developed outside of commercial activities.
As a free time developer I will not be physically able to meet any of those timelines, my free time is more important to me then ever, so don’t push me.
Going forward, i will continue to focus on what i love. Kernel/u-boot development, so feel free to use my kernel and u-boot as you see fit. However, I’ll be changing one of my main packaging helping, anything not in packaged in Debian, well “you” have to get it in Debian.
To the best of my knowledge (not a lawyer), over the last year I’ve tuned my image builder to meet EU CRA requirements for our downstream manufactures.
Robert, you’re an absolute legend, and definitely one of the good guys.
Don’t lose any sleep over the EU CRA. Their intention is not to go after people like you.
I’m super impressed you’ve made efforts already to comply with this, especially while not even living in the EU. Hugely appreciated!
I don’t know if it was with regards to this specific piece of legislation, or something else I’ve forgotten about, but I believe Linus’s approach was “Lets just wait and see, and focus on developing tooling that can automatically help all open source projects achieve compliance”
sorry it took me some time to get familiar with the whitepaper itself. It contains information how Raspberry Pi is compliant with CRA in form of points and tables and what are the remediation methods for the customer
voodoo@21-am335x-bbb:~$ sudo apt-get install debsbom
Reading package lists... Done
Building dependency tree... Done
Reading state information... Done

<snip>

0 upgraded, 179 newly installed, 0 to remove and 0 not upgraded.
Need to get 139 MB of archives.
After this operation, 531 MB of additional disk space will be used.
Do you want to continue? [Y/n]
Install via pipx
sudo apt update
sudo apt-get install pipx
Add to path if never done…
pipx ensurepath
source ~/.bashrc
Install
pipx install debsbom[spdx]
Much smaller
voodoo@21-am335x-bbb:~$ du -sh ~/.local/share/pipx/venvs/debsbom/
26M	/home/voodoo/.local/share/pipx/venvs/debsbom/
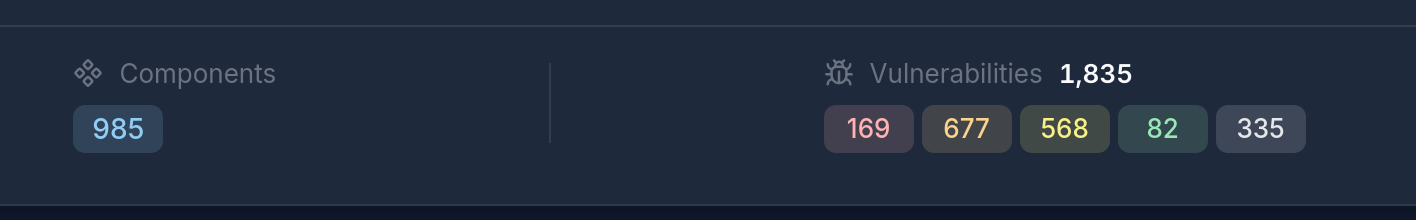
Hey Robert, do you have any recommendations for the analyzer tool to search for the vulnerabilities? I tried to use self-hosted Dependency Track but didn’t have any luck. It consumed the SBOM but it didn’t find any vulnerabilities in any of the components
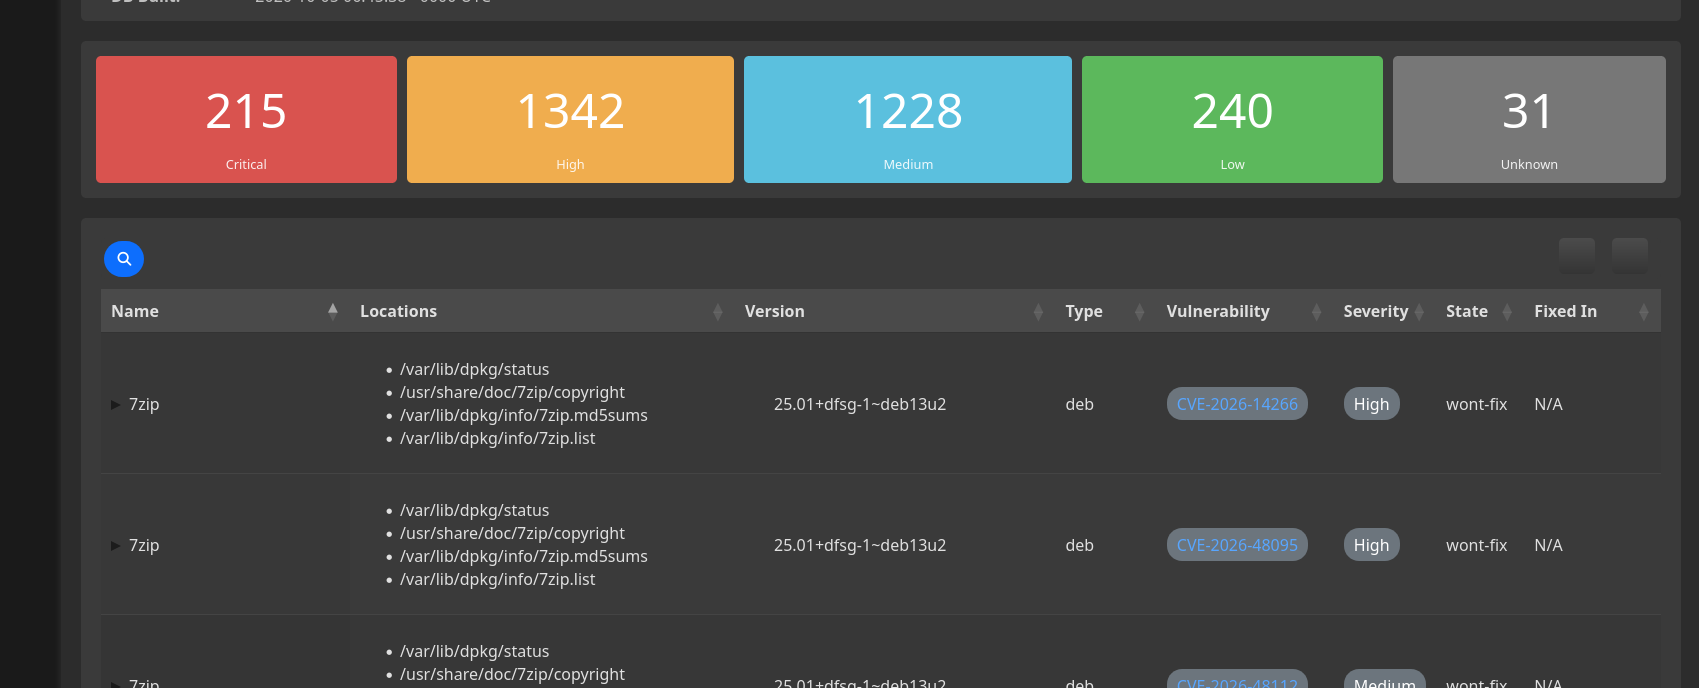
I need to dig more into it, as it seems to be scanning every linux module and creating a match, but it can’t figure out what kernel version to tie the cve to…
But yeah, right now most of the scanners are pretty useless, i’m just glad we can run grype locally to test sbom files..